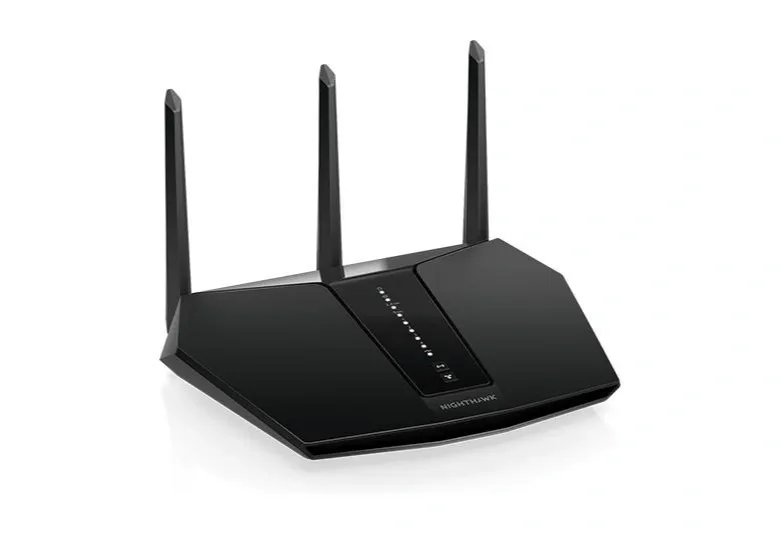
Check the model label if you use a NETGEAR Nighthawk router. NETGEAR lists six models containing PHP components affected by the PHP2Shell investigation. Its advisory still names no fixed firmware, and the actual impact remains under review. The company describes access through local web management by someone already connected to the Wi-Fi network or LAN.
The models in NETGEAR’s assessment
- RAX28
- RAX29
- RAX30
- RAXE290
- RAXE300
- CAX30
The advisory, last updated October 28, rates this exposure Medium. NETGEAR says the management interface is not accessible from the internet by default and reports no evidence of attacks targeting these devices. Those statements describe its assessment, not a guarantee about a router whose configuration has been changed.
NETGEAR says no other product or service is exposed based on its assessment. Check the exact model instead of treating every Nighthawk or Orbi device as affected.
PHP exploitation and router exploitation are different findings
PHP2Shell refers here to CVE-2026-109618 and CVE-2026-109619 in PHP, software used to serve web requests. Microsoft’s security response guidance reports that CISA added both to its Known Exploited Vulnerabilities catalog on October 26. Exploitation of PHP in other systems does not establish that these Nighthawk models have been compromised.
The local access condition is a useful distinction for a home owner. It still leaves a reason to limit who can join the network.
Limit access and watch for model-specific remediation
NETGEAR’s stated precaution is to keep untrusted users off your Wi-Fi network. Review who has the main password and change it if it has been shared with someone who should no longer have access.
A guest Wi-Fi network can separate visitor devices from your main network when configured appropriately. The PHP2Shell advisory does not establish whether every guest-network configuration blocks access to the management interface. Do not treat enabling a guest network as a verified fix.
Keep installing firmware recommended for the exact model. A release note saying only that it addresses security vulnerabilities does not identify a PHP2Shell fix. Automatic firmware updates are useful on supported devices, but still check the installed version and the advisory for an explicit remediation statement.